SecretHive — a self-hosted key vault
A small, self-hosted key vault for the secrets services and scripts need: vaults of versioned secrets and certificates, pages for people and an API for tools; a command line that writes them as files on a host at deploy time; a PowerShell module for the session that needs one; CI jobs that read with their own identity and store no key; and an audit trail of every value read.
Status 2026-10-11: in use, in production. Server 0.14.2, command line 0.14.0, PowerShell module 0.1.0.
Since 2026-10-11 every compose stack on our two hosts gets its secrets from it. MIT licence. The source and the images are not public yet.
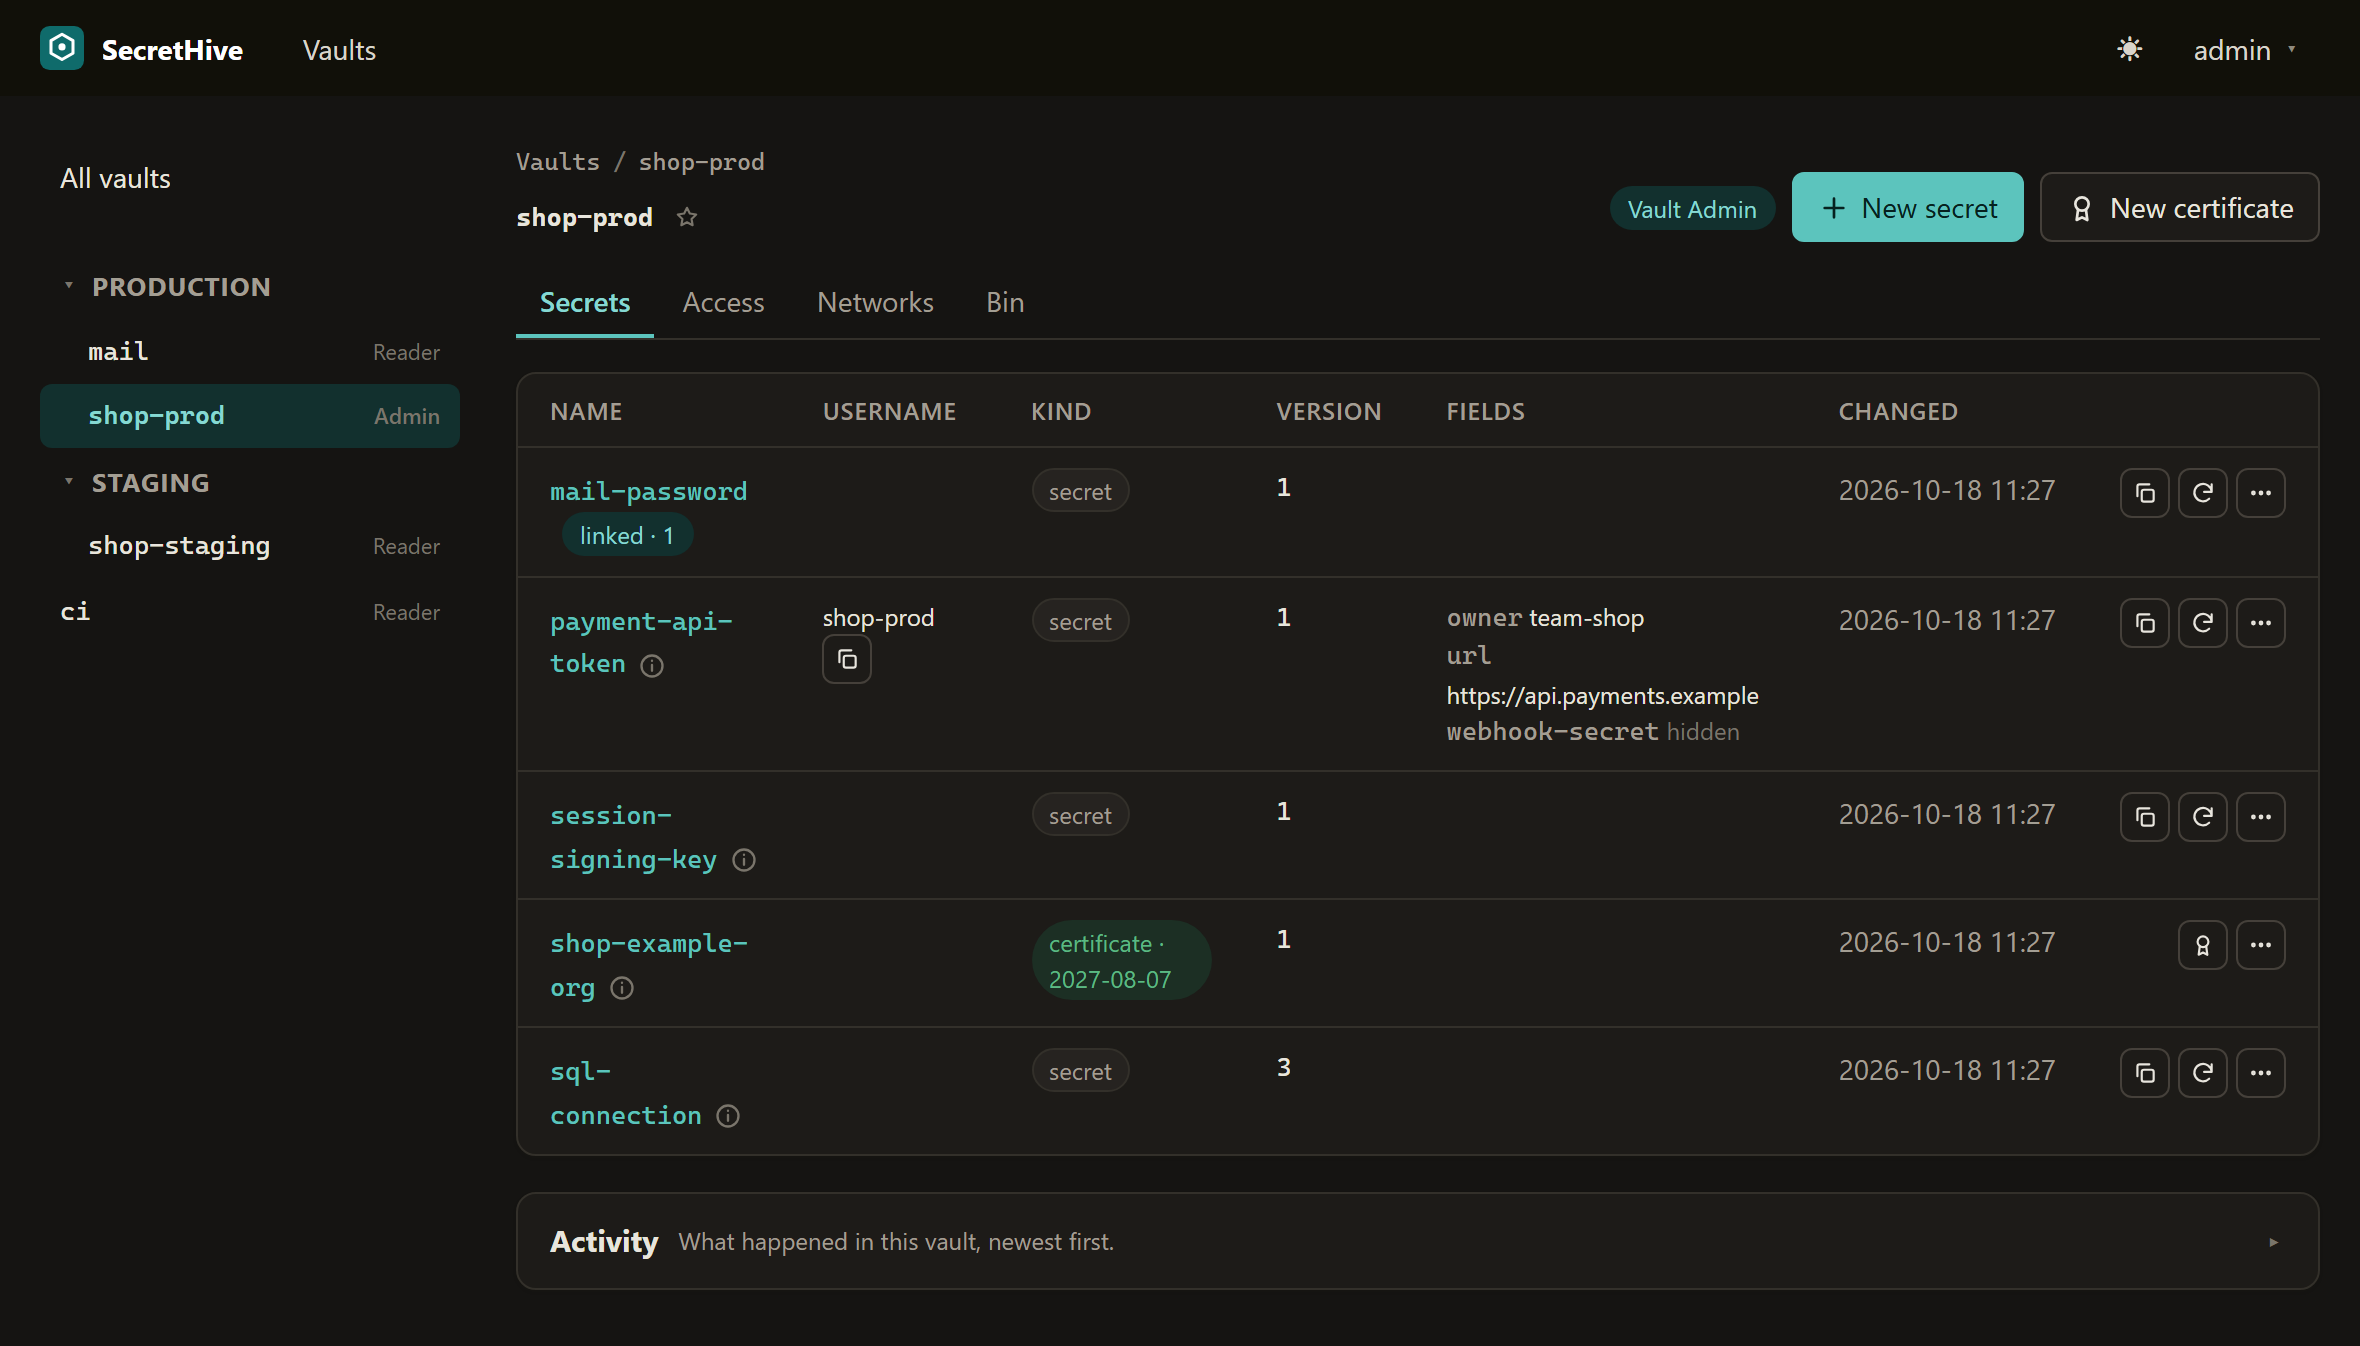
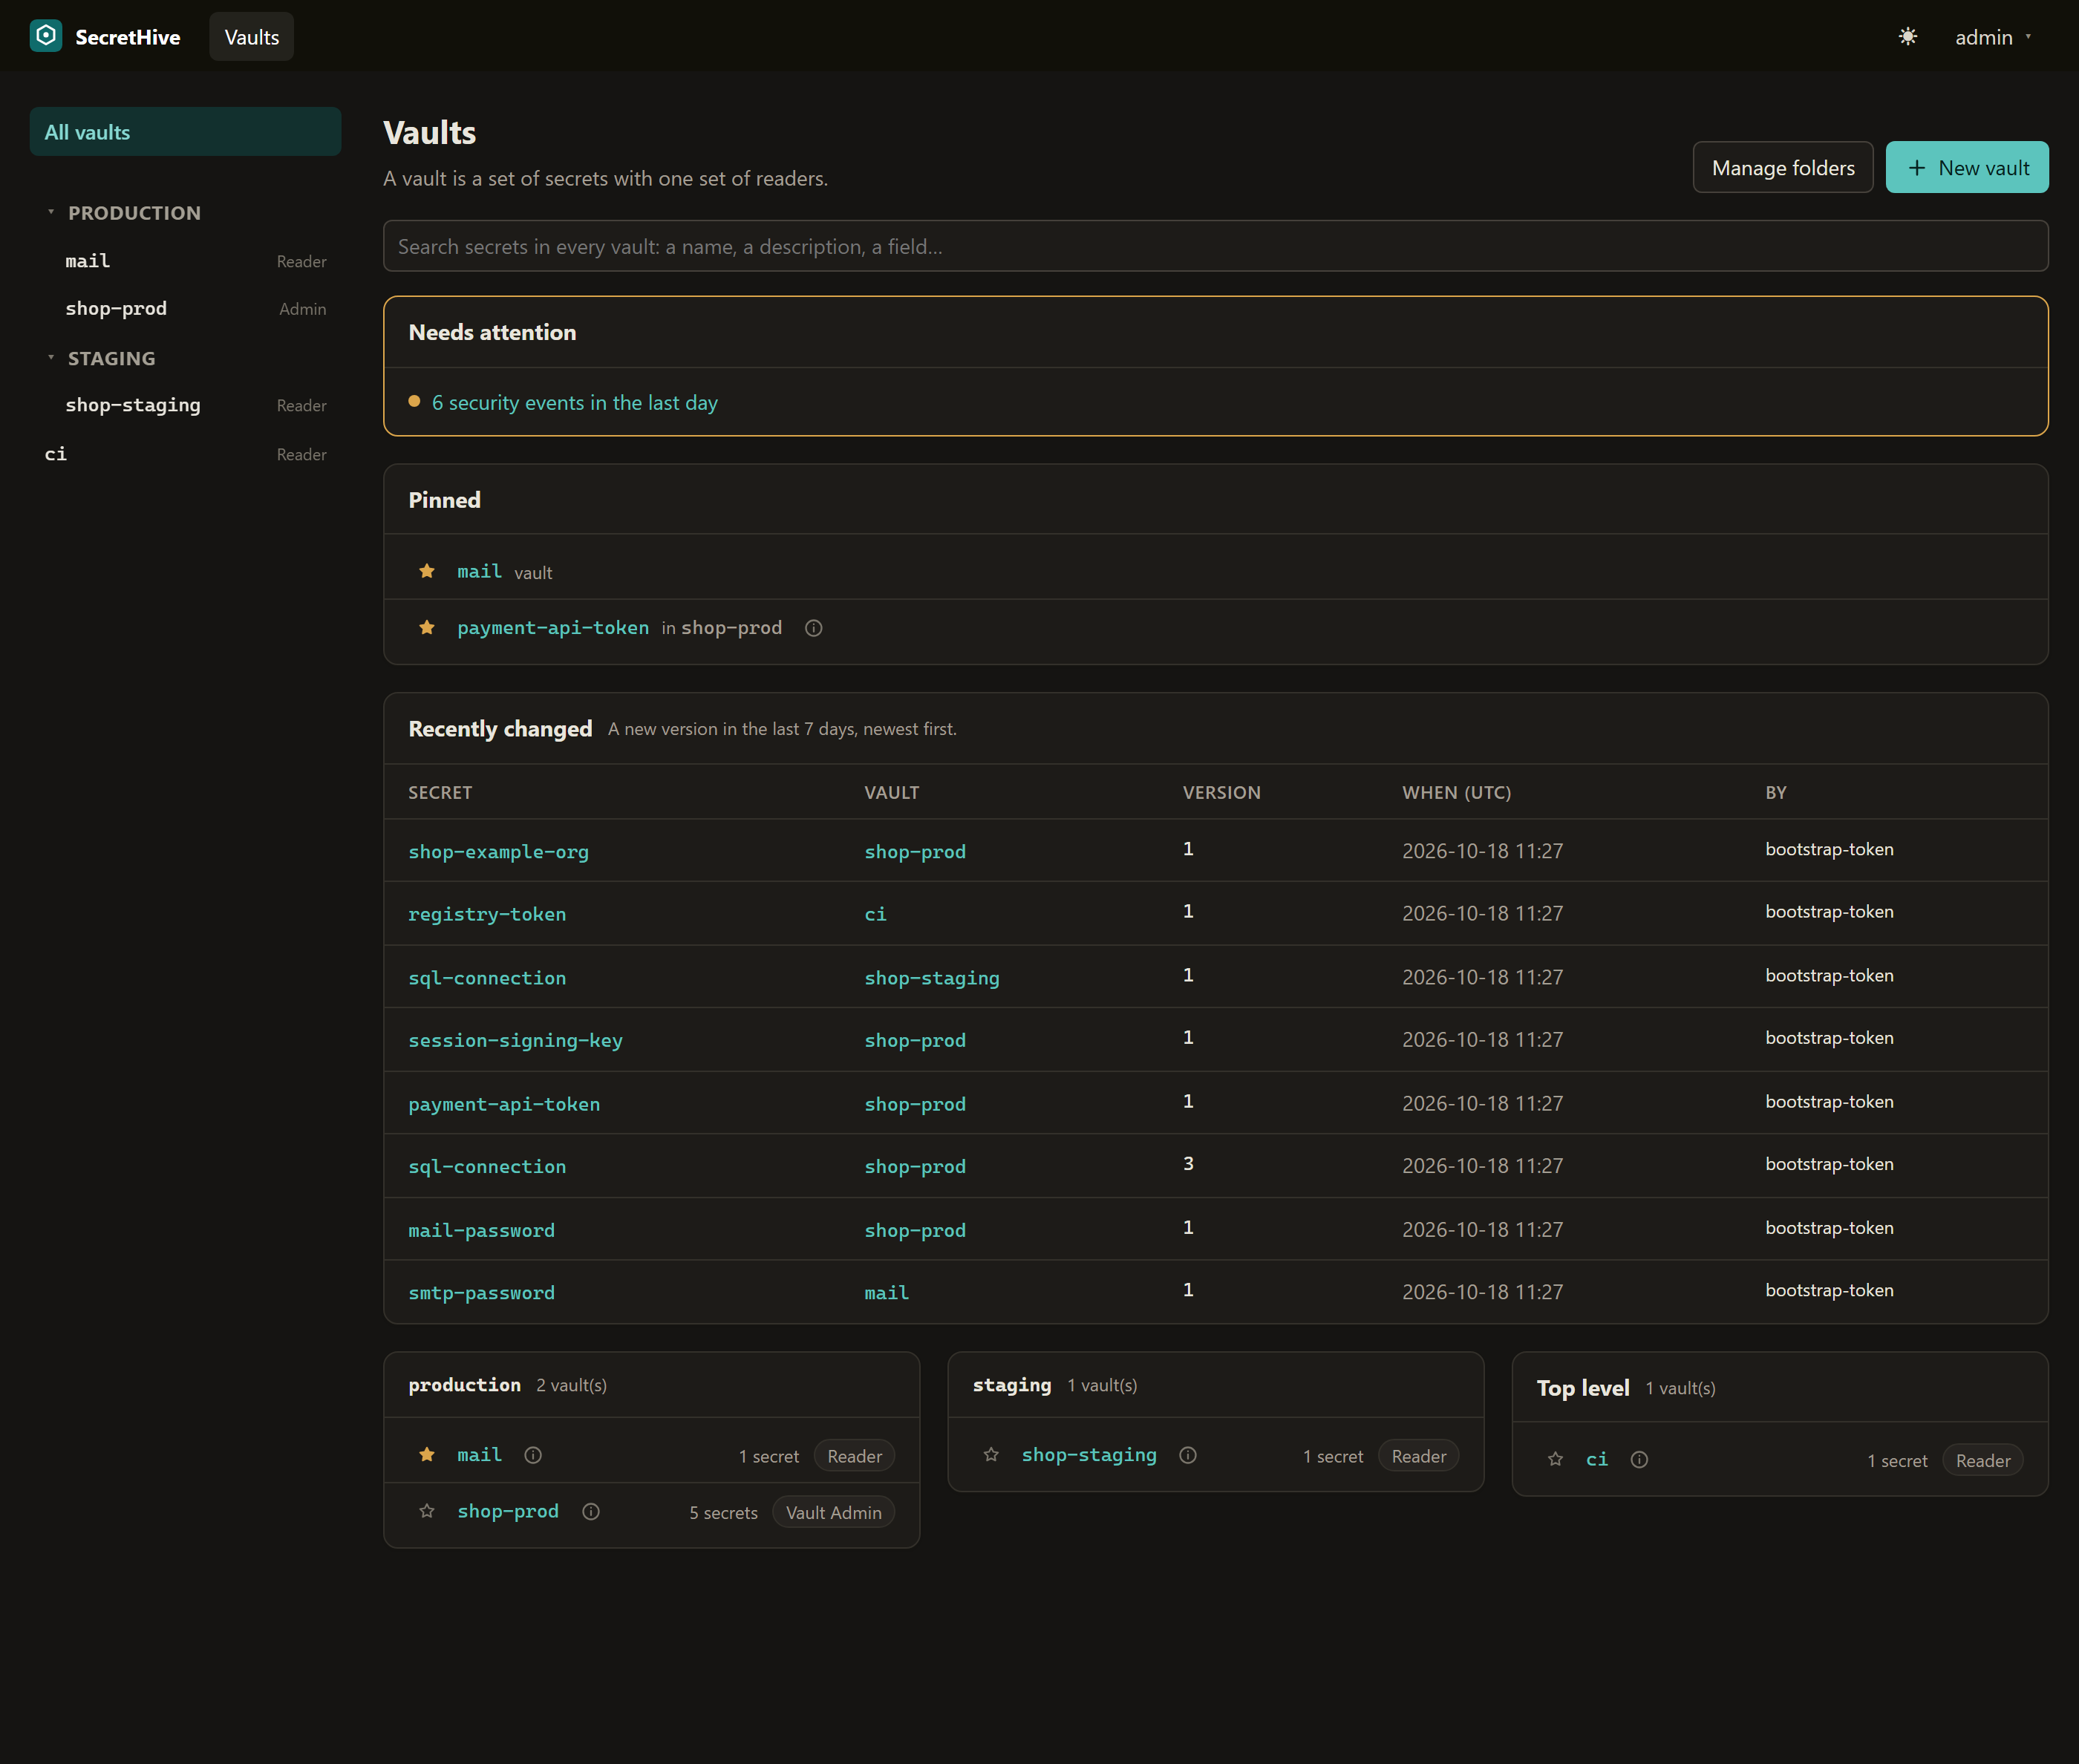
These pages describe release 0.25.0 of 2026-10-18. New since 0.21: a generator for a new value; a home page with what needs attention,
pinned vaults and secrets, recent changes and the vaults by folder; a vault's pages in three columns (the vaults
in their folders, the list, one secret beside it), a Username column, and folders of vaults whose roles count in
every vault beneath them. New since 0.14: the account, service identity, key and group
routes of the API, a search across vaults, certificates in bundle push, running without the bootstrap token,
a new version keeping what it does not name, a key's highest role changed in place, a key without an end date
(with a warning, and on record), the role Secrets Writer that sets values and reads none, and a PowerShell module (0.2.0) that also sets values.
Why we built it
Our homelab runs a few dozen services on a handful of hosts, and its secrets lived where each tool happened to put them: an environment file per compose project on each host, secrets stored in the forge for CI, and a password manager for the keys people use. That works until you ask the questions a vault exists to answer. Which services use this token? Who read it last? When was it changed, and what breaks if we change it now? A value copied into three files gets rotated in two.
What we wanted from a vault, all at once:
- Secrets in one place, grouped into vaults, versioned, with a way back from a delete.
- Fetched by the tools already in use, at deploy time: a shell, a compose file, a CI job, PowerShell.
- Machine identity without a stored secret where the platform already issues one, and keys done properly where it does not.
- Sign-in with the identity provider we already run, rights per vault, and reading a value as a right of its own.
- Every value read on record, in a form a monitoring system can alert on.
- Proof that it can be restored before anything depends on it.
- One container that runs on a NAS with SQLite, and with SQL Server where there is one.
The options we looked at each covered part of that list. The capable ones bring an operating model sized for a platform team; others keep single sign-on, network restrictions or audit streaming for a paid edition. SecretHive is the part we need, built on the same foundations as our other applications, and nothing more.
What sets it apart
Reading a value is its own right
Seeing that a secret exists, when it changed and what fields it has is one role (Reader); reading its value is another (Secrets User). Every value read is an audit record: which secret and version, who, through the pages or the API, and from which address. Being an administrator of the server is not a role in a vault. An administrator sees every vault as a Reader, because they hand out the roles. They can always reach a value, by giving a role to themselves, to a group they are in or to a machine whose keys they make; each of those routes is a security event in the audit trail, and that trail is the control. See Roles, keys and networks.
A new secret and a new version can have their value generated: a length (32 by default) and symbols on or off.
The symbols leave out what an .env file, compose or a shell would read twice ($, quotes, backslash, backtick, #).
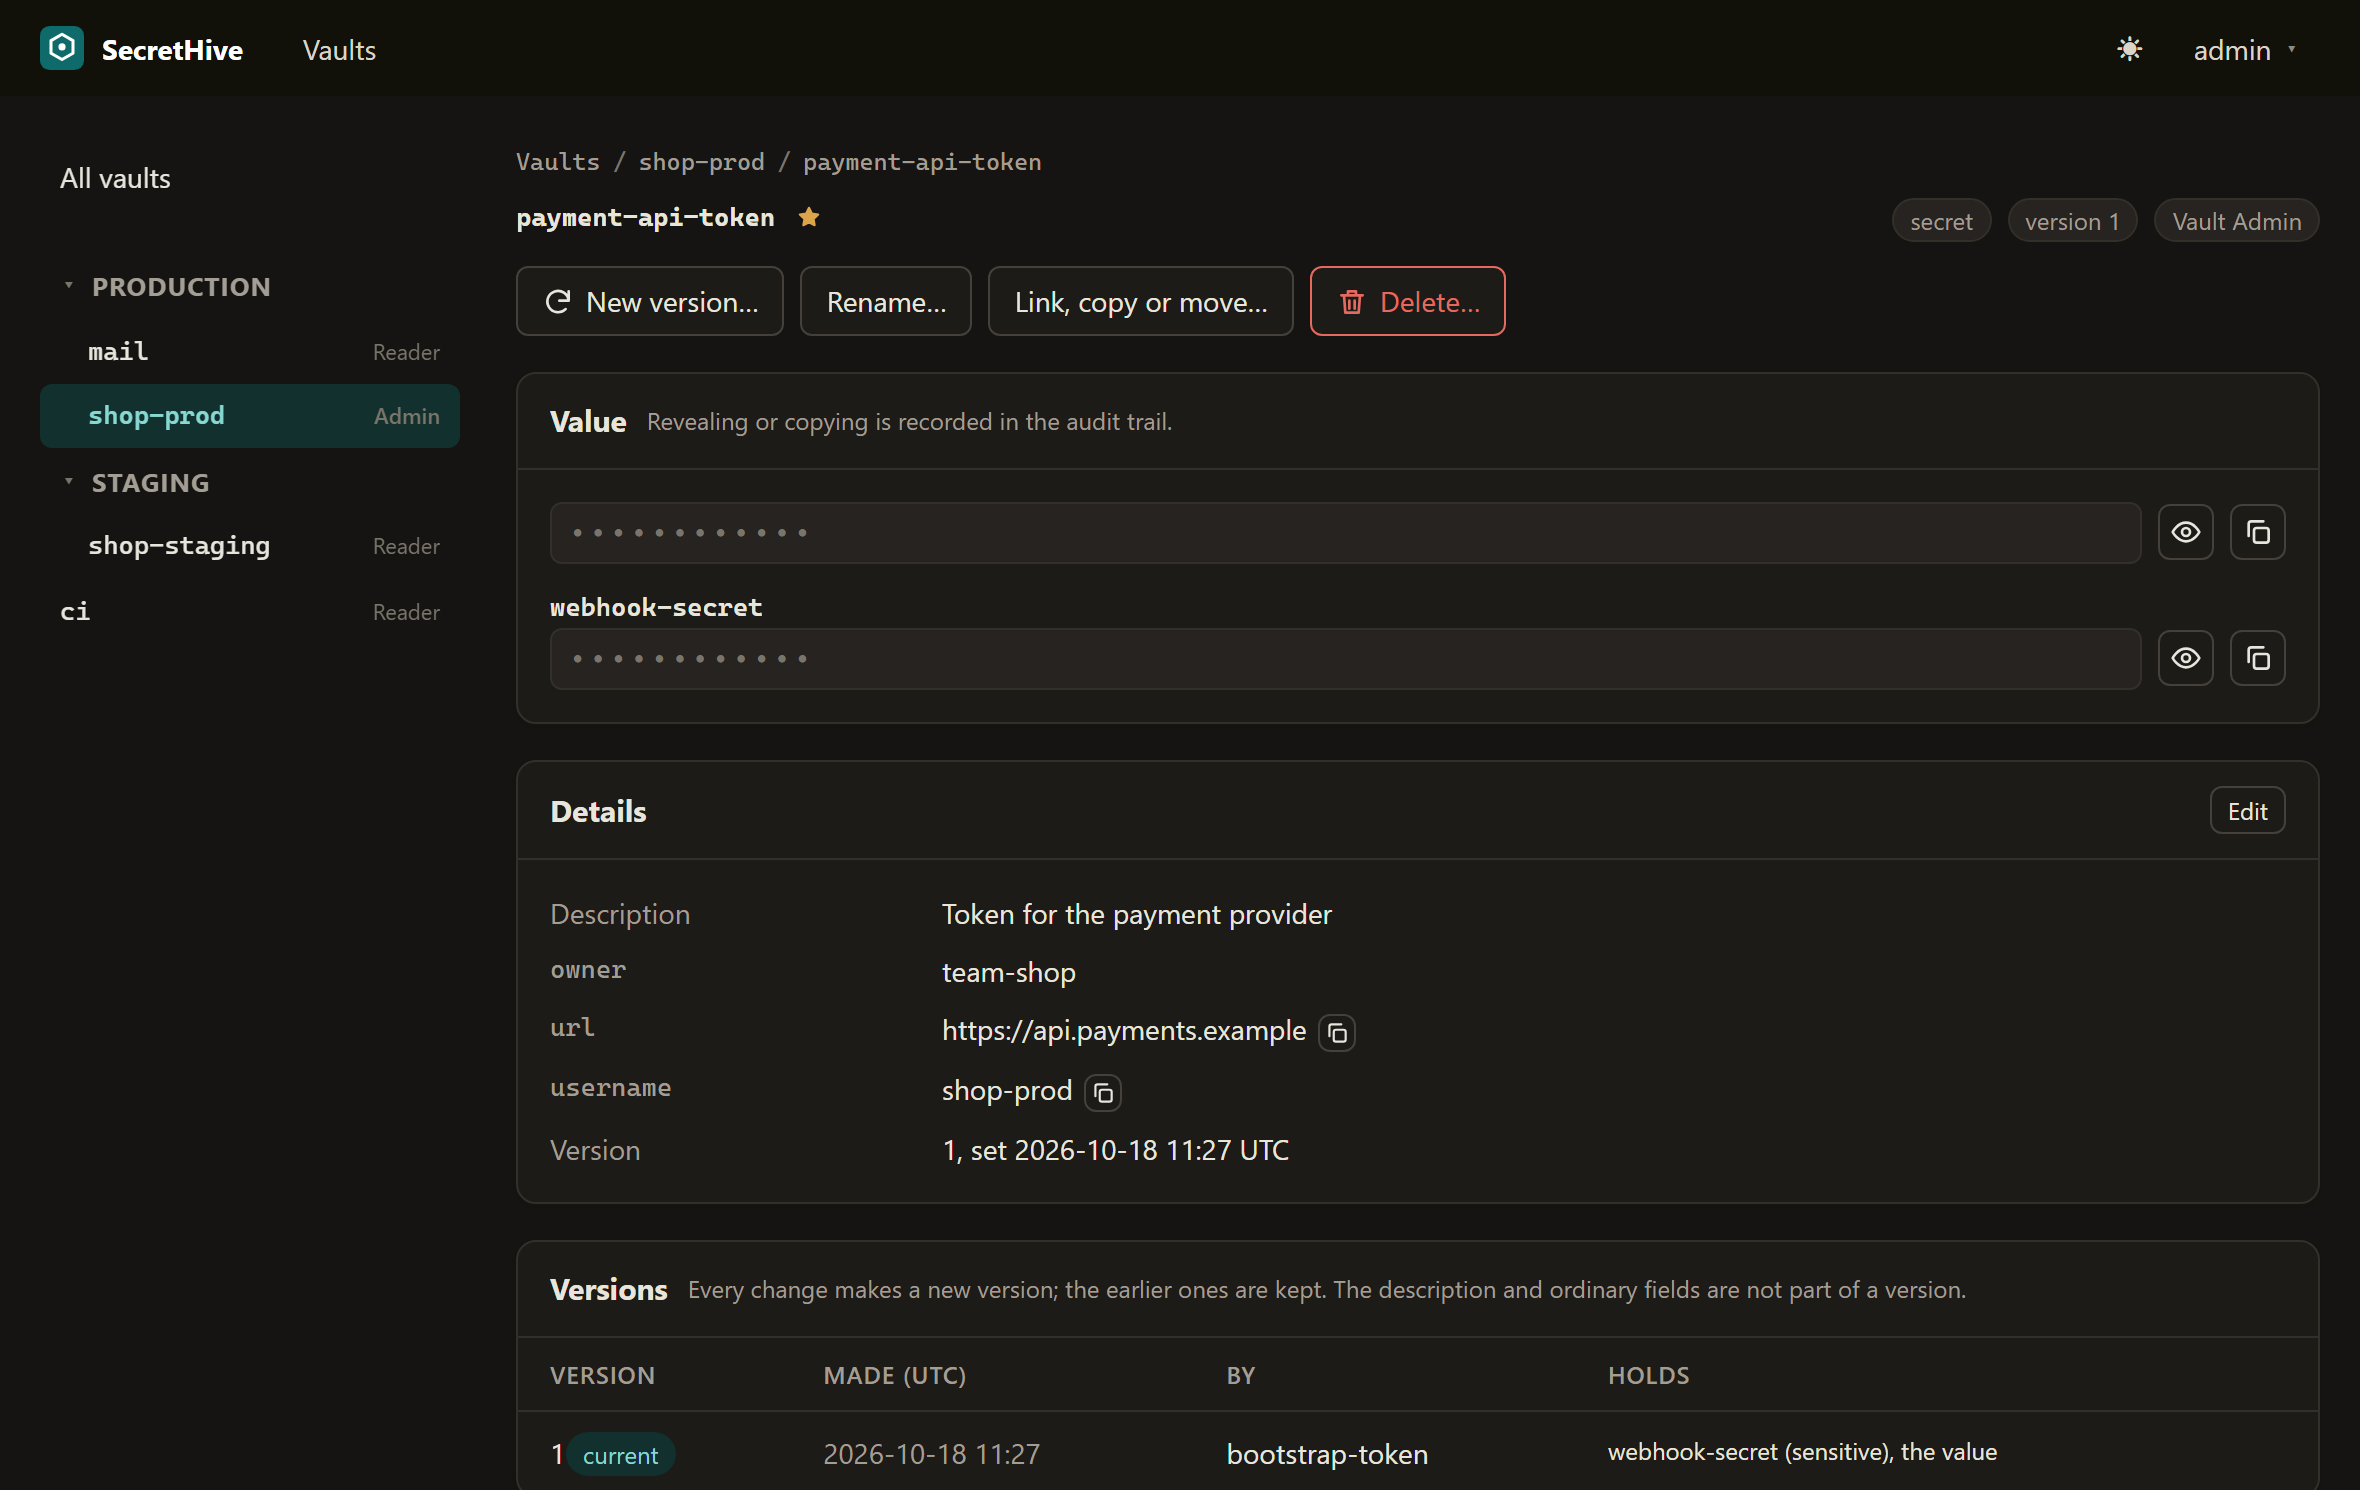
What can be done to a secret is a row of buttons under its name (a new version, rename, link, copy or move, unlink,
delete), each in a dialog. The vault's list offers the same per row: copy the value, a new version, and the rest
behind "more". A copy from the list is a value read like a reveal, and on record; an ordinary username field has a
copy button of its own and is no read. Only what your role allows is offered. In the list and in the search
results, a secret with a description has an (i) after its name: point at it, focus it or tap it to read it.
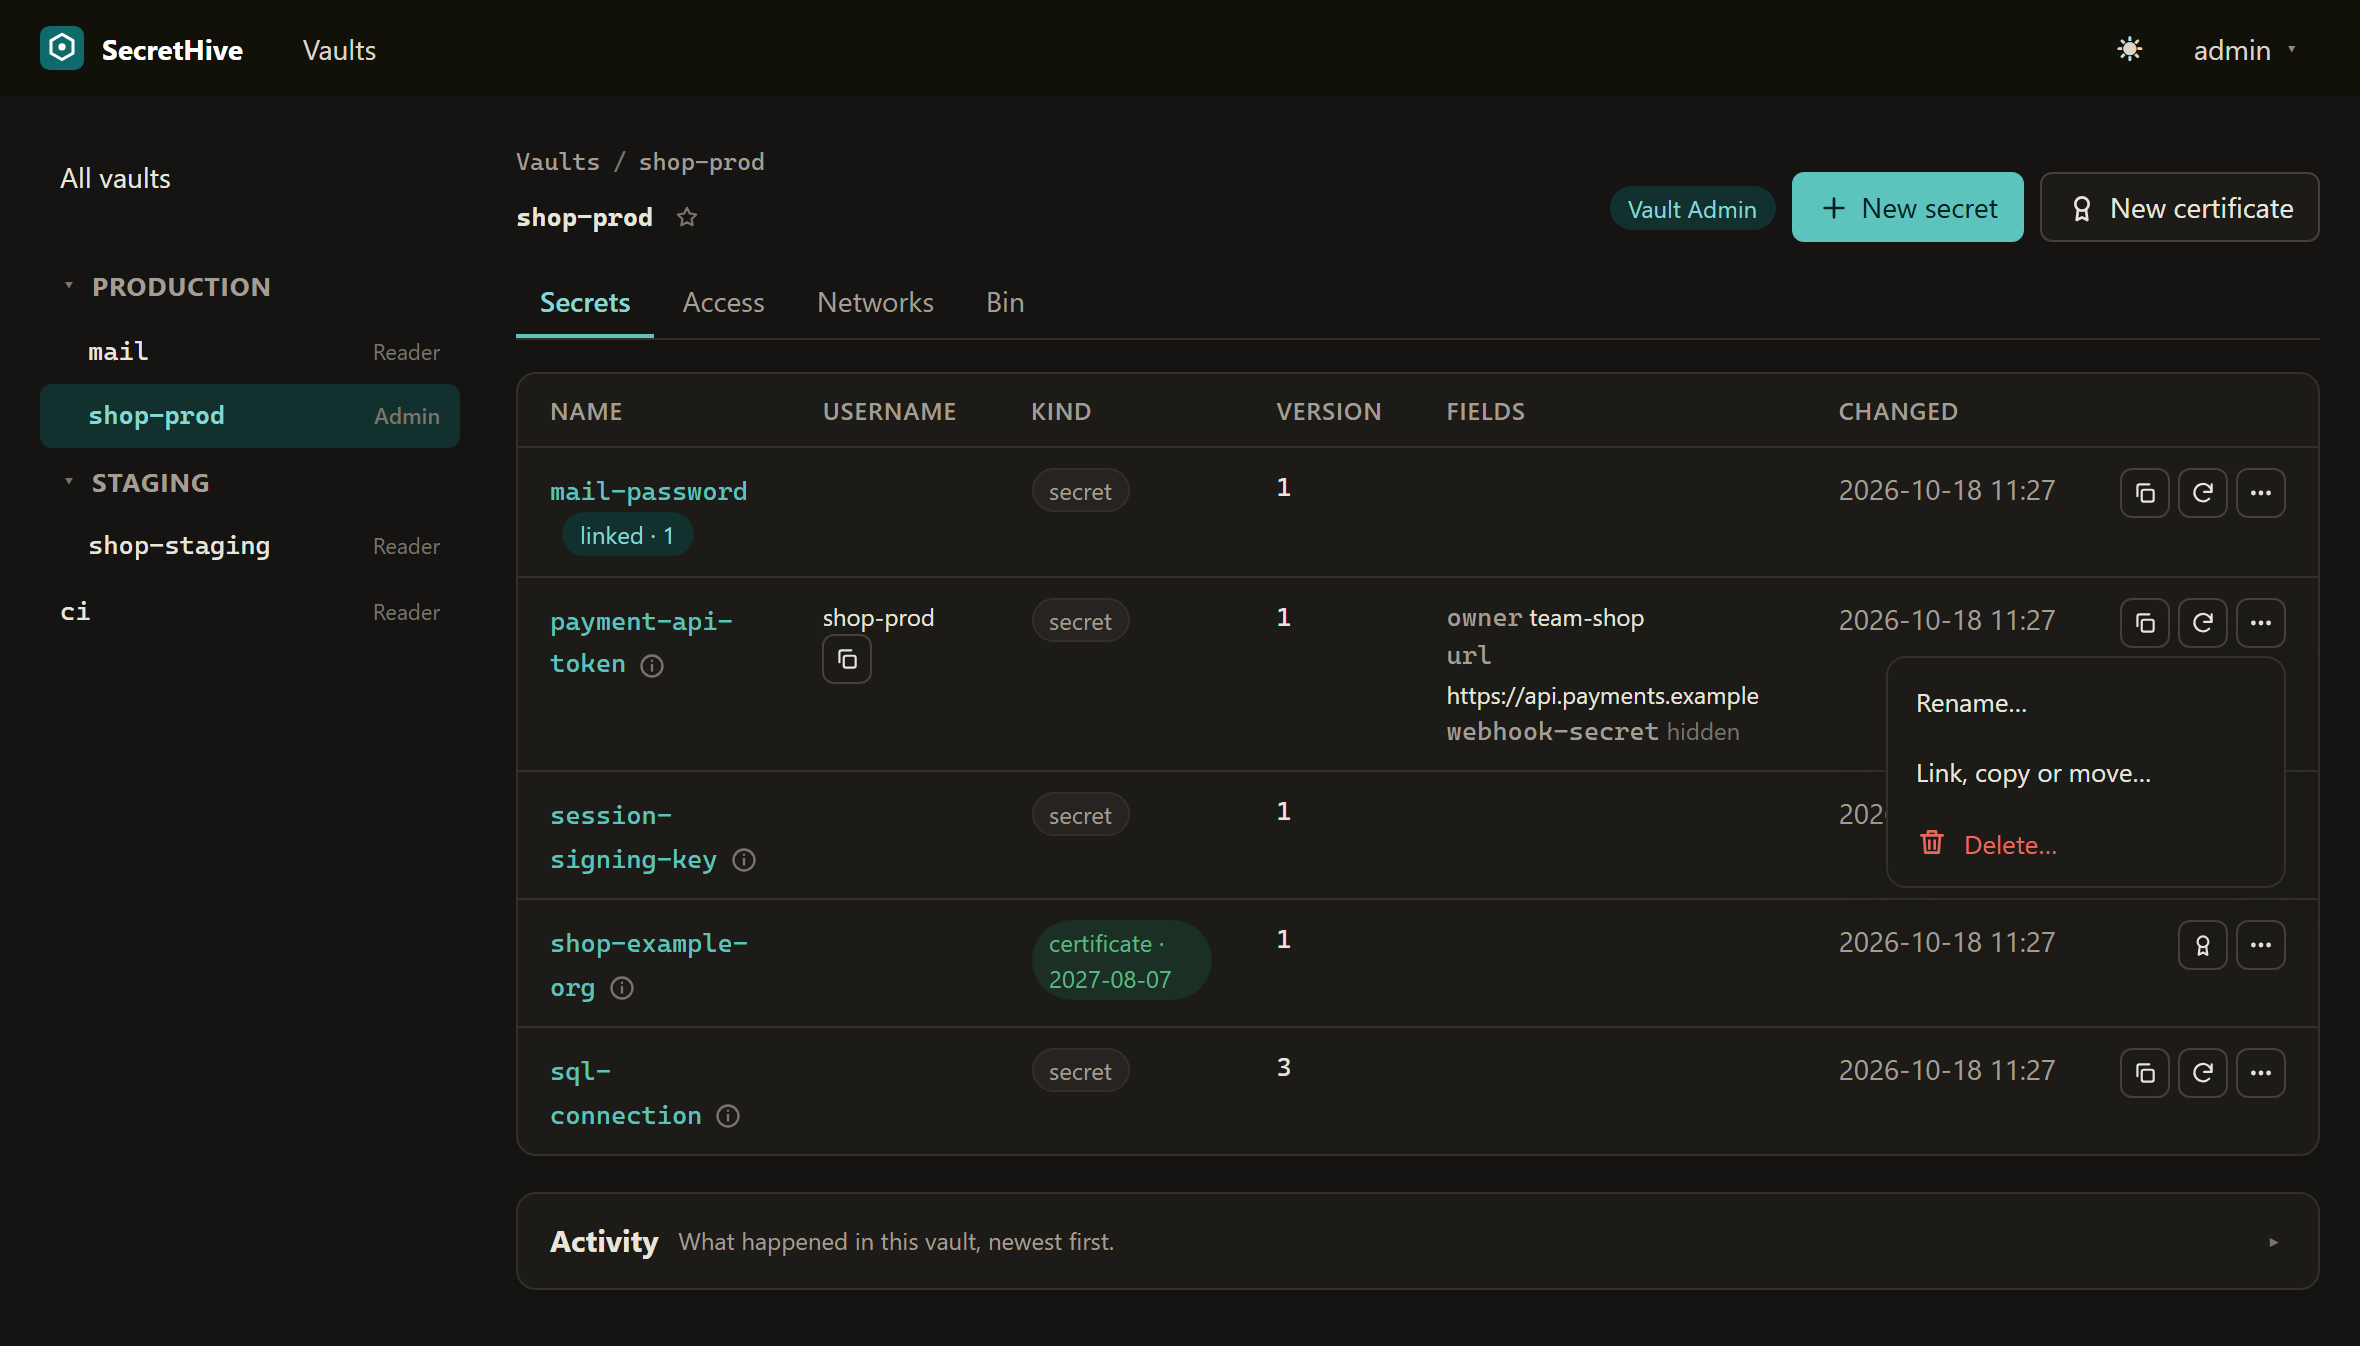
A name in the list opens the secret beside it, without leaving the list: its actions, its value and sensitive fields (a reveal is the same recorded read), its details and its last events. The address names it, so a link or a refresh keeps it open; the arrow keys go to the one above or below, Escape closes it. Editing the details, the versions and the whole history stay on the secret's own page. The vaults you have a role in are beside every page of a vault, in their folders, and on a phone in a menu.
The home page starts from the same place: the search across every vault, then what needs attention (a certificate that ends within 30 days, a key of yours that ends within 14; for an administrator also the keys of service identities, a backup that was not read back, and the security events of the last day), what you pinned (a star on a vault or a secret, kept per account and seen only by you), what got a new version in the last week, and every vault in a card per folder with your role and how many secrets it holds. A section with nothing in it is not shown.
Machines authenticate as what they already are
A CI job presents the short-lived token its platform signs for it, and SecretHive is told to trust that platform. What the job may read comes from the repository named in the token. Nothing is stored for the job anywhere, and taking the repository out of a vault ends its access at the next request. See CI jobs without a stored key.
Where that is not possible, a key is a first-class credential rather than a shared password: it belongs to one identity and is audited under it, is shown once, expires, can be limited to one vault, to a highest role and to listed networks, and an identity can hold two at once so a rotation breaks nothing.
Built for the host, not around it
secrethive render writes the secrets a compose project needs as one file per key, for applications that read
/run/secrets, from a manifest in the compose repository that holds no values. Files are replaced whole, with the
owner and mode the container needs, and the command says which containers to restart. The host reads from the server
when it answers and from a bundle sealed for that one host when it does not, so a deploy never depends on the vault
being up, and a refusal is never worked around. See Secrets on a host.
Certificates are not just another secret
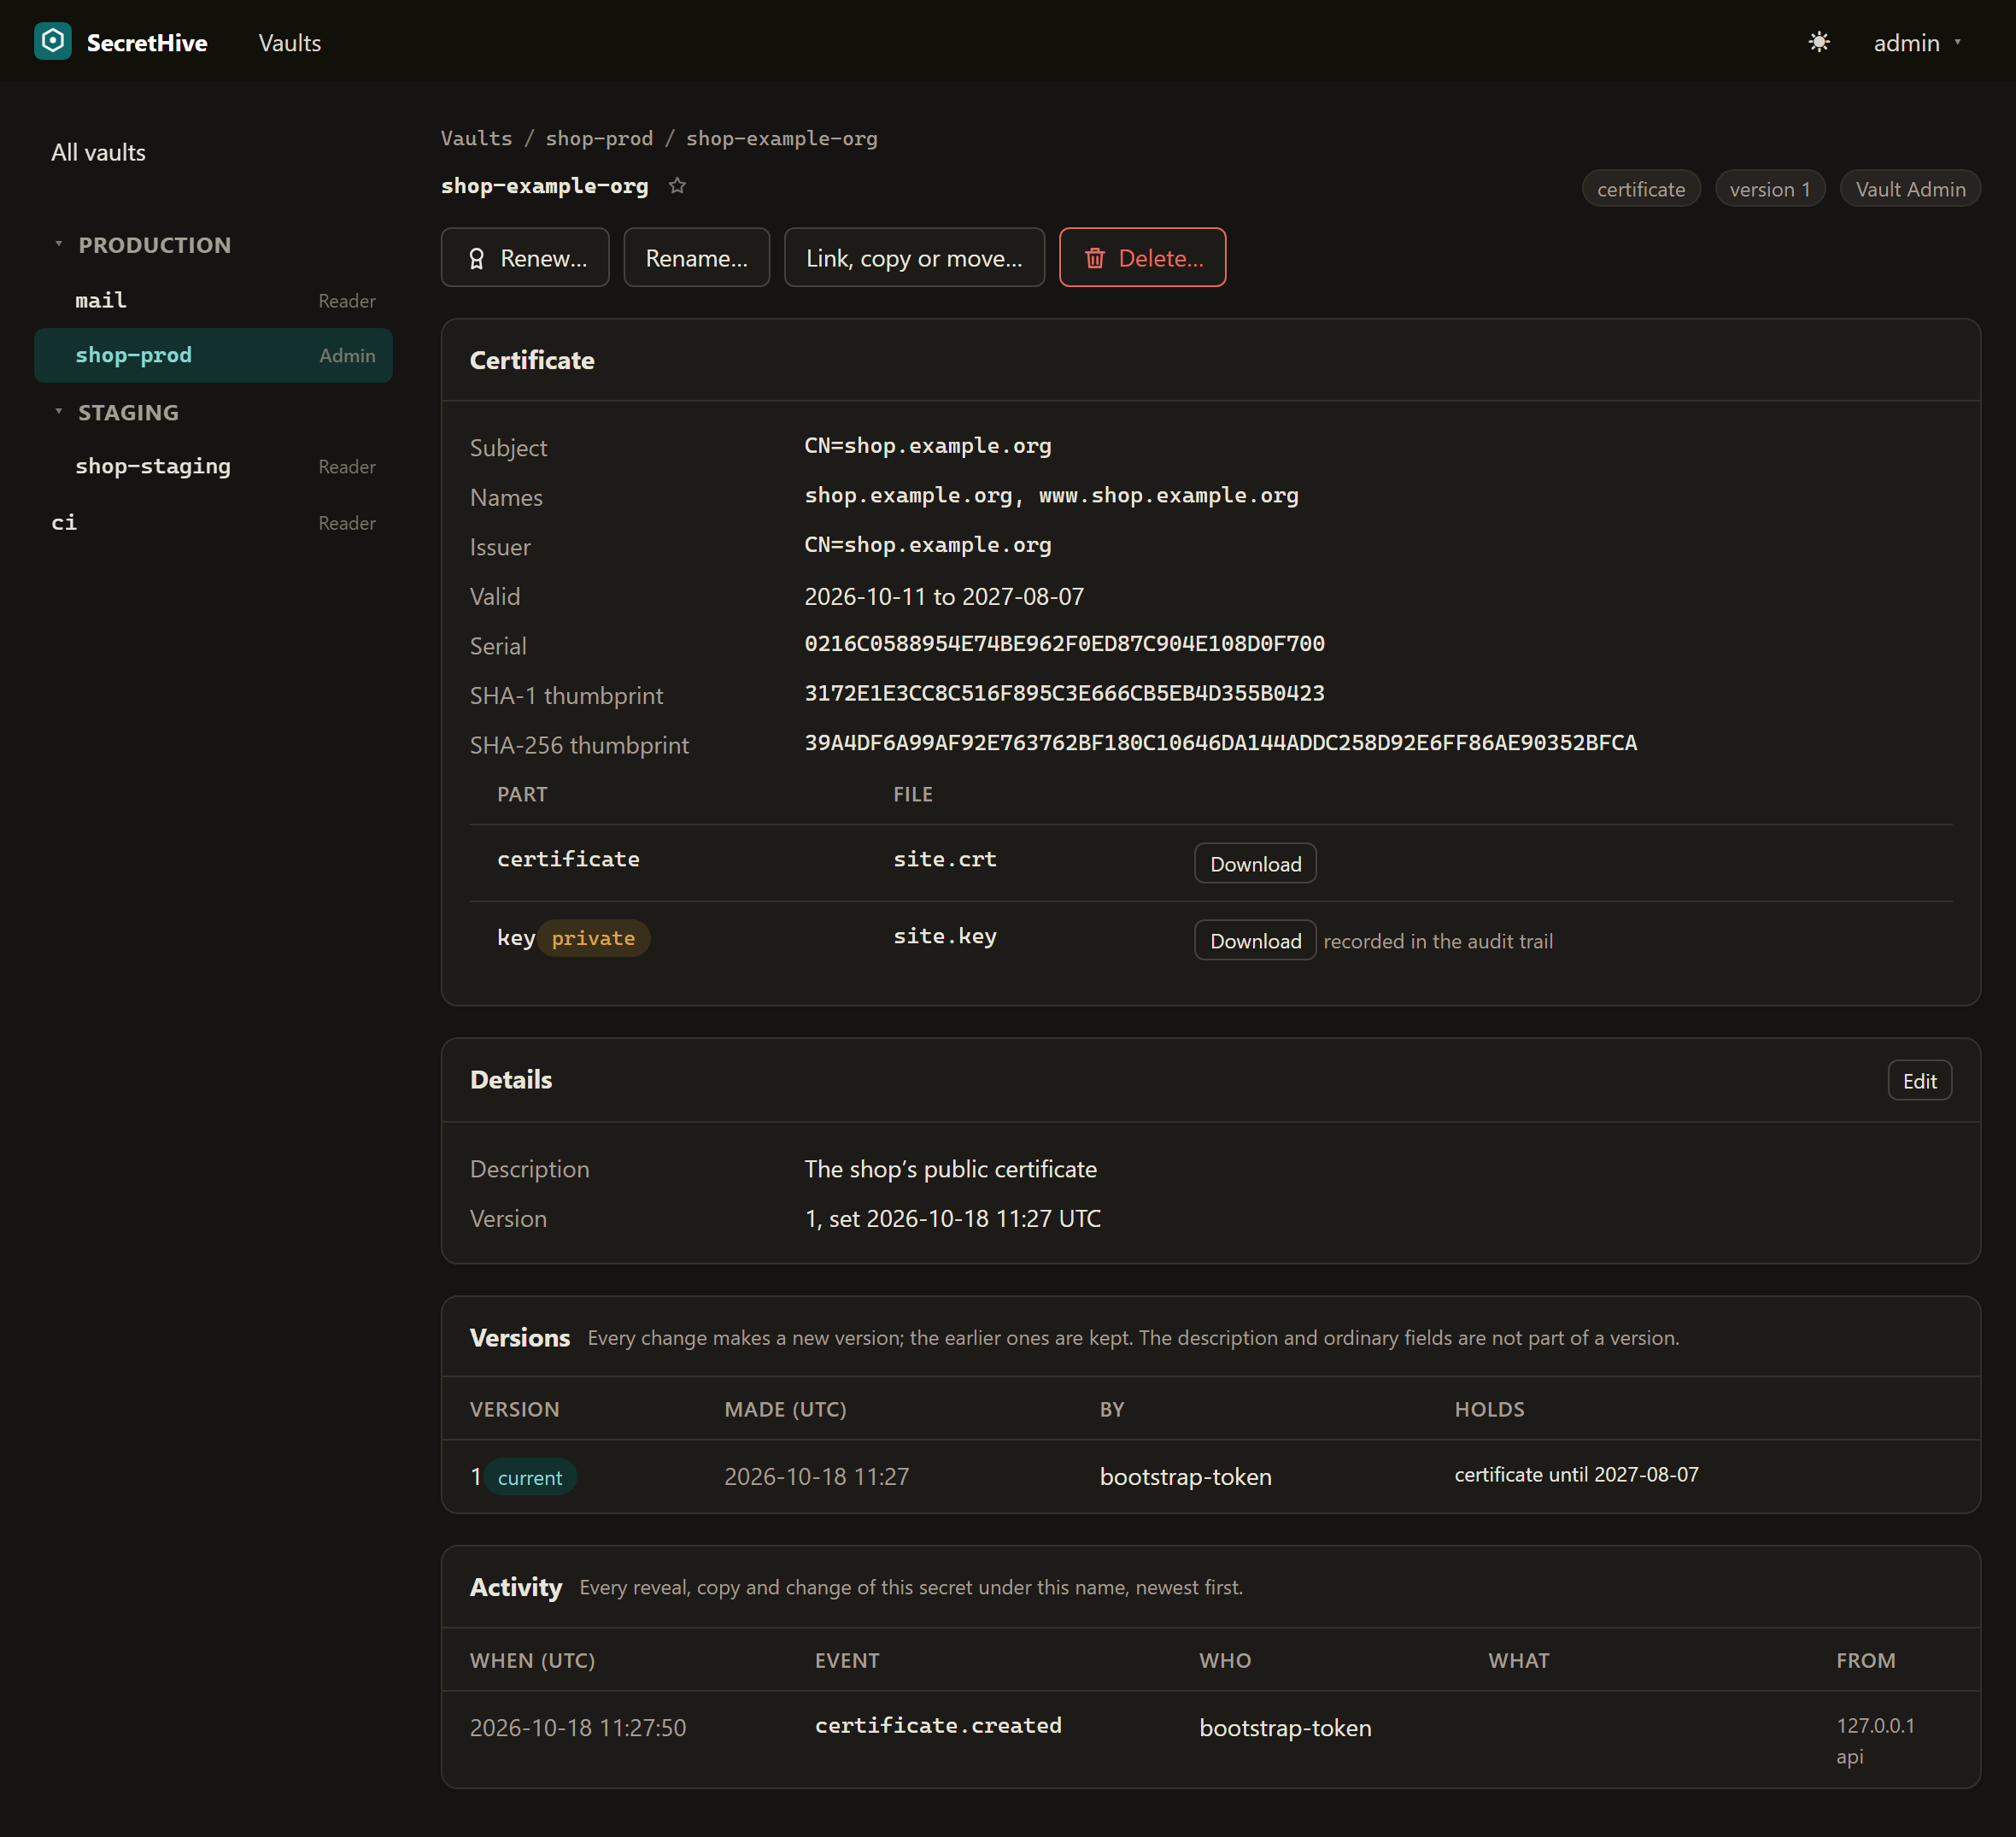
A certificate is one object with several parts: the certificate and its chain, the private key, a PKCS#12 file and its password. Reading a part is an audited read like any secret value. Subject, names, issuer and expiry are read from the certificate itself, a part that does not belong to the others is refused, a renewal is a new version under the same name, and an approaching expiry is an audit event at 30, 14 and 3 days. SecretHive stores and watches certificates; it does not issue them.
Recovery before trust
The server makes a backup of its database every day, verifies it, and keeps the last fourteen. A backup is sealed, so a changed file is refused, and the master key is never inside it. Restoring is one command into an empty database, also from SQLite into SQL Server, and that runs with the shipped image on every build. The health endpoint reports the age of the last verified backup. The master key can be replaced with one restart, and people stay signed in. See Running in production.
Your identity provider
Local accounts, and OpenID Connect against any provider, several at once, set up on a page without a restart. Groups, with groups at the provider feeding SecretHive groups, and five roles per vault. See Sign-in with Authentik.
Safe by default
- Nothing is anonymous, on any vault, ever.
- Every version of a value is encrypted with a key of its own, and those keys with a master key held outside the database.
- A vault and a key can each be limited to listed networks. Networks are kept as named groups, defined once and used wherever they apply.
- Values never appear in logs. A value has no text form in the code; a test lists the few files that may open one, in the server and in the command line, and fails the build when another does; and every build greps the shipped image's log and data folder for the values it stored. No command takes a value as an argument.
- Every audit row is also a structured log line, so the trail can leave the host as it is written.
- Events that should never pass quietly carry a security severity: a refused network, a refused key or token, a new link between vaults, a purge, a stale backup, a replaced master key.
At a glance
- Vaults of secrets with versions; every earlier version can be read and made current again
- A search across every vault you have a role in: by name, description or an ordinary field, never by a value
- A description and extra fields on a secret, each either ordinary or sensitive
- Certificates as their own objects, with expiry events
- Folders of vaults: a role given on a folder counts in every vault beneath it, and a move says on record who gained and who lost
- Move a secret to another vault with its history, copy it with a record of where the copy came from, or link it so two vaults hold one value under their own names and a change reaches both
- A bin per vault, with a page of its own: a delete never destroys, whoever may change secrets in the vault can restore, and automatic emptying is off until an administrator switches it on; purge protection per vault
- A REST API for tools: vaults, secrets and their versions, access, accounts, service identities and their keys, groups, networks, sign-in providers, backups. A browser session can read through it and changes nothing; what belongs to a person's own session stays on the pages: their profile, their password and their own keys
- A command line for hosts:
render,check,status,run, and a sealed bundle withpullandpush - A PowerShell module for Windows PowerShell 5.1 and PowerShell 7: read, set, search, credentials
- Tokens from a trusted issuer for CI jobs; keys owned by an identity
- An audit trail with a page, as JSON log lines, and over OpenTelemetry; a health endpoint with facts to alert on
- Backup, restore and master key rotation
- Light and dark, and theme packs
Where it runs
One container image for linux/amd64 and linux/arm64, non-root, working under an arbitrary user id:
- A single container with SQLite and a local volume: a NAS, a small VM, a developer machine. This is the mode it is designed around, and how we run it.
- With SQL Server where there is one. The storage and restore tests run against both databases, and every build starts the shipped image against both.
Not built
Said plainly, because an earlier version of this page promised them: an Ansible collection, registration as a PowerShell SecretManagement vault, a stand-alone emergency export, an External Secrets recipe for Kubernetes, and one-time sharing.
Name
SecretHive: it keeps secrets, and it sits alongside the other Hive applications.